PHP2Shell: No login, no app code, no warning. What next?
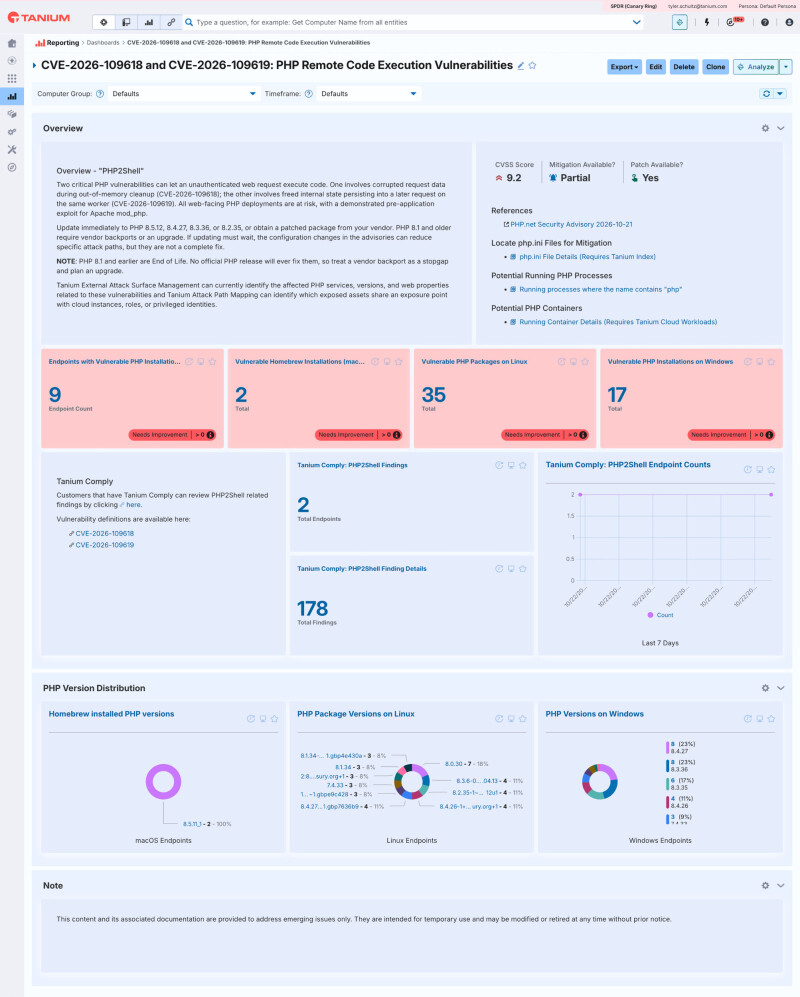
PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 patch two critical flaws (CVE-2026-109618 and CVE-2026-109619) rated 9.2 CVSS severity. The vulnerabilities enable attackers to execute arbitrary code via HTTP requests without authentication, affecting all earlier versions. Exploitation in the wild has been reported. The challenge lies in identifying and patching every PHP instance across diverse server environments (PHP-FPM, mod_php, php-cgi, FrankenPHP, LiteSpeed).
Key points
- Critical remote code execution flaws in PHP core affecting all versions before patches
- CVSS 9.2 severity; no authentication required for exploitation
- Active exploitation reported; reliable public exploits emerging
- Finding all PHP instances across environments poses patching challenge
Summary and key points written by AI from the headline and a short excerpt, so they can be incomplete or wrong. The Register did the reporting; read the original for the full story.
Read the full story at The Register