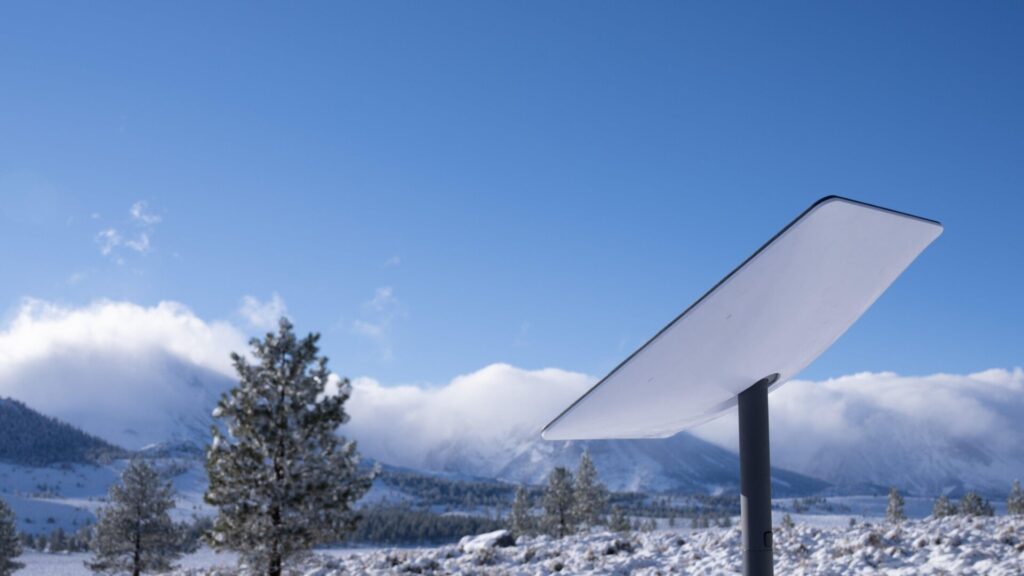
Researchers Uncover Signs of Massive Surveillance Operation on Starlink Users
Researchers identify evidence of a large-scale surveillance campaign targeting Starlink users, particularly in nations where the service is prohibited or limited.
Cloud, cybersecurity, SaaS and B2B innovation.
Researchers identify evidence of a large-scale surveillance campaign targeting Starlink users, particularly in nations where the service is prohibited or limited.
A credit card skimming group compromised an analytics script used by e-commerce platform Convertr to steal customer payment data during checkout.
Security researchers report that PHP2Shell vulnerability patching is moving too slowly despite critical severity, with 93.6% of systems still exposed five days after disclosure.
An autonomous AI agent discovered four critical vulnerabilities in EPICS industrial control software within four hours, including a 9.8-rated remote code execution flaw.
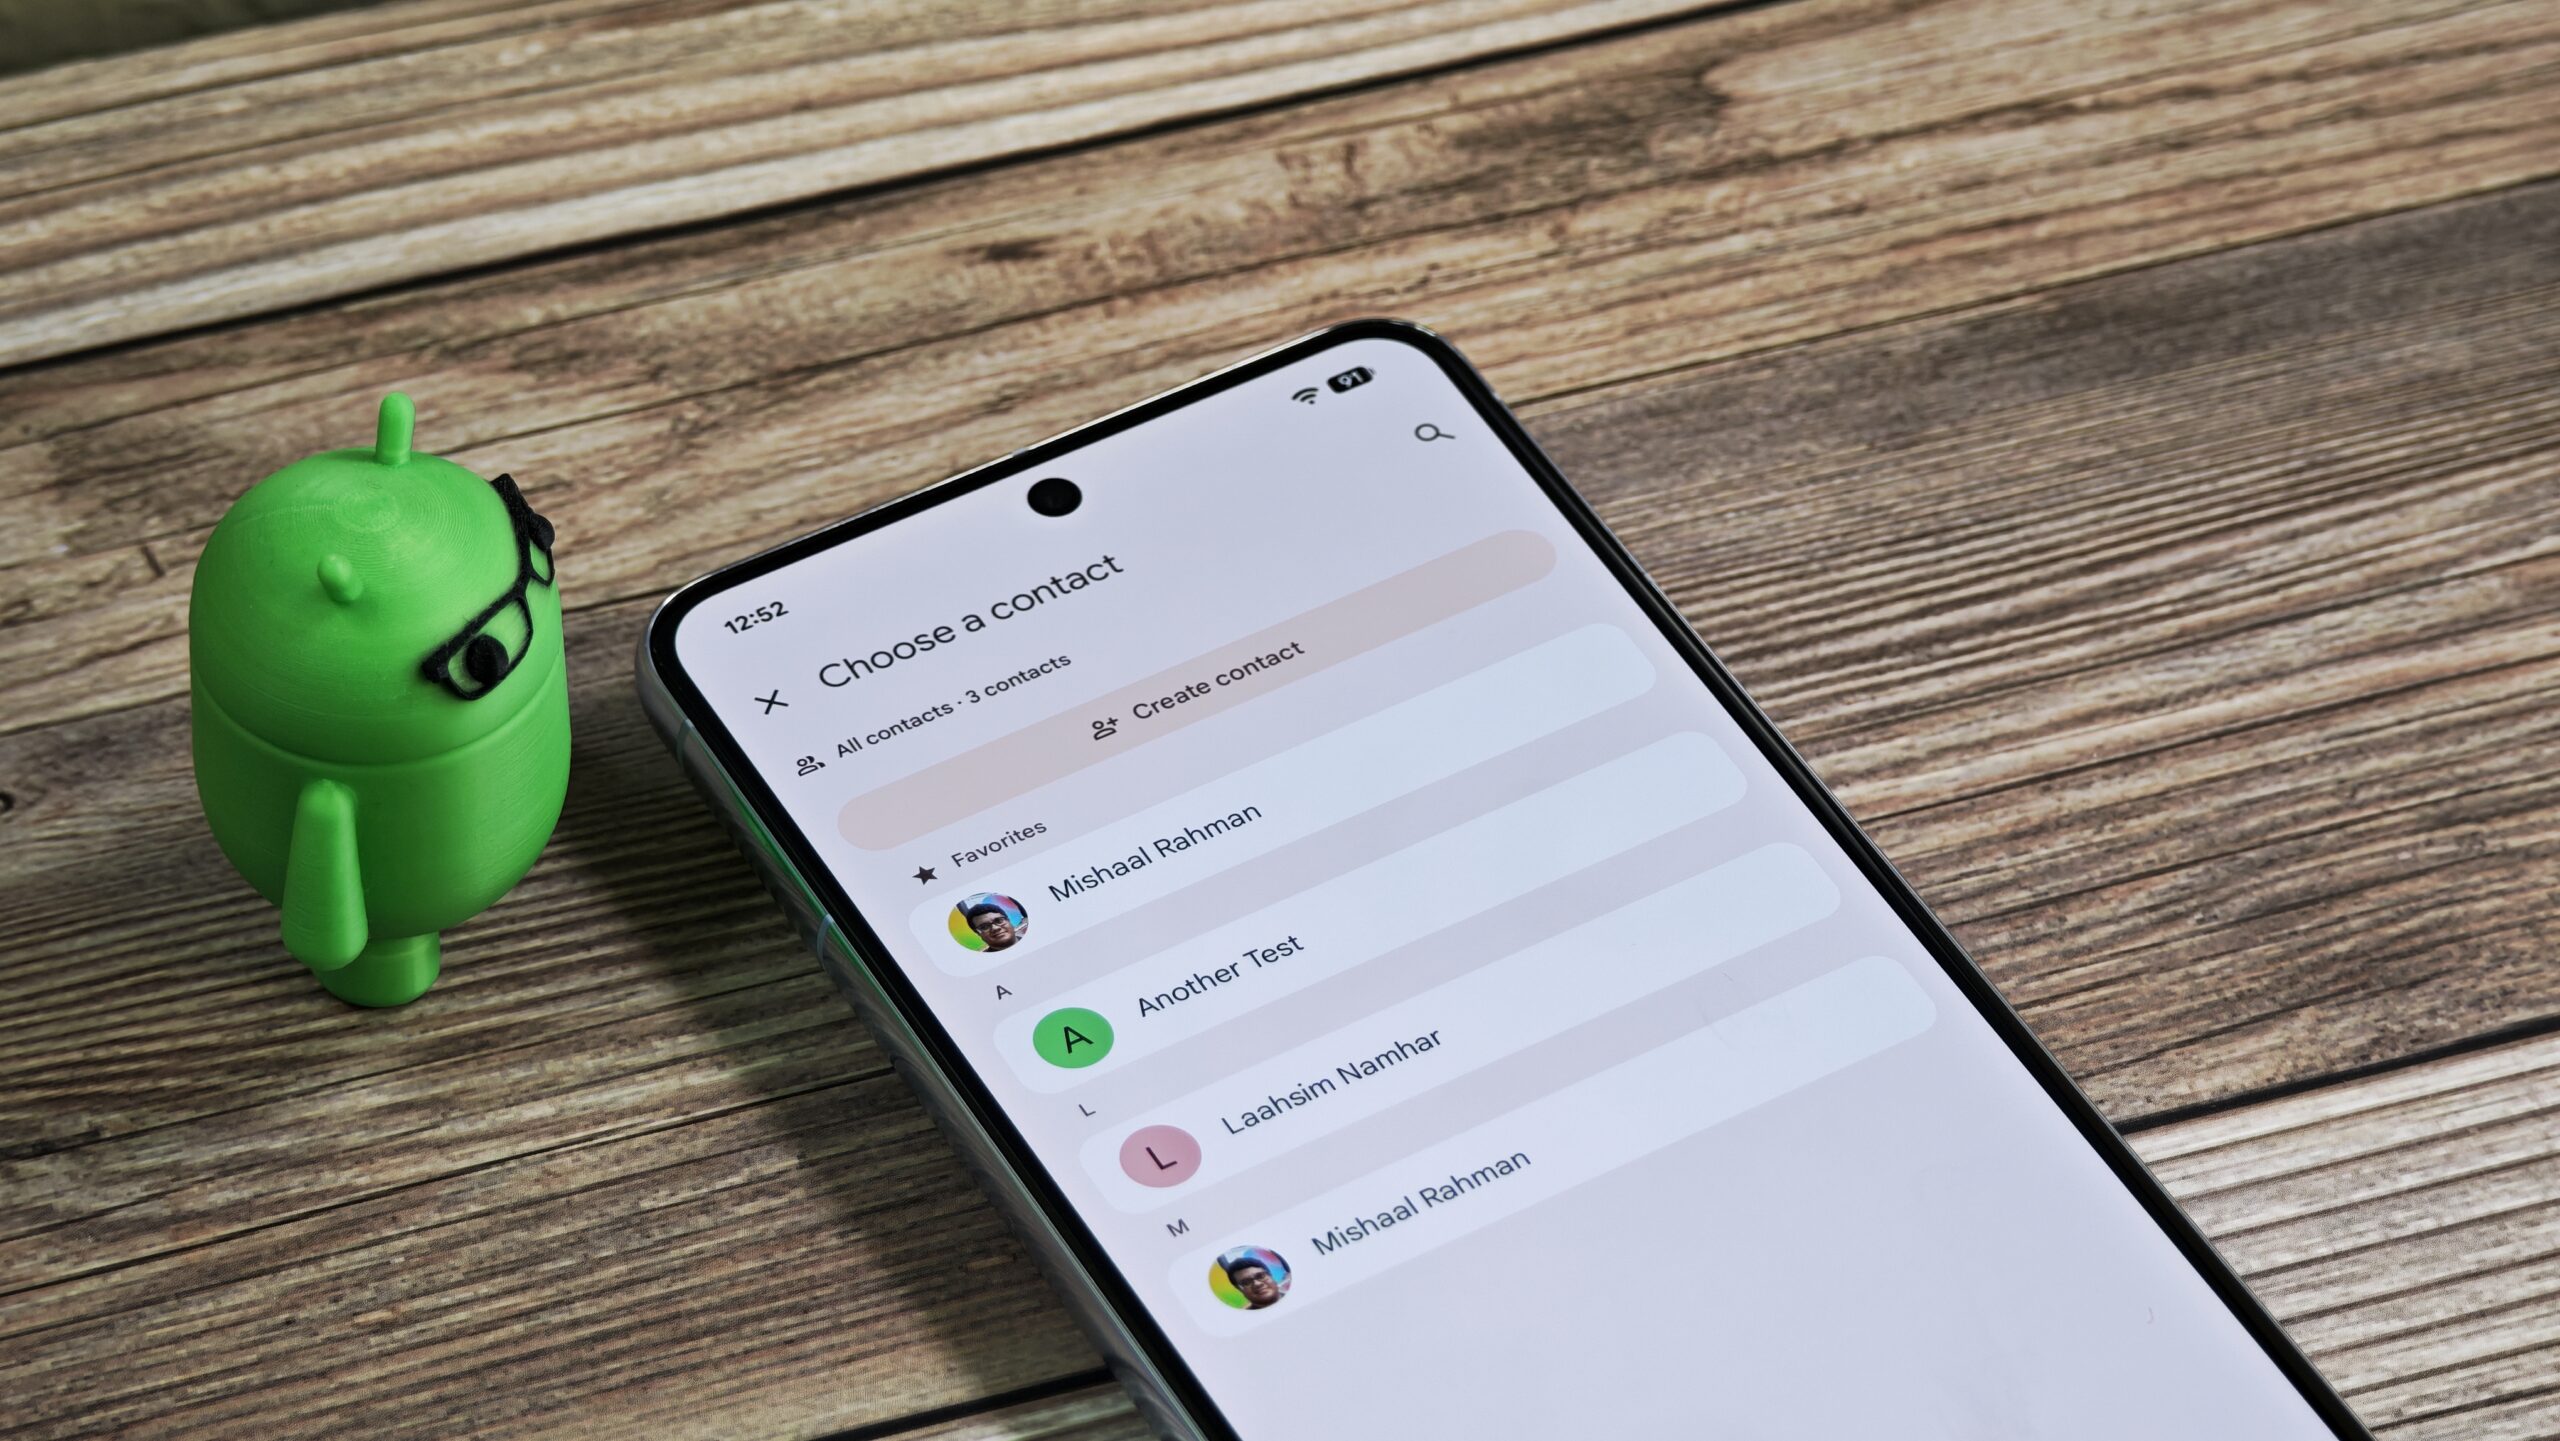
Google is implementing more granular contact permissions in Android 17 QPR2 to limit app access to bulk contact edits.
Cathedral, a cybersecurity startup founded by former DOGE staffers, claims it broke into Anthropic's internal systems in less than 12 hours by exploiting vulnerabilities in enterprise software. Anthropic confirmed the white-hat breach and has since closed the access points.
Microsoft and other companies are addressing a critical 'HTTP2Shell' vulnerability in Node.js that could affect millions of websites.
AI is uncovering new security vulnerabilities in web infrastructure faster than they can be patched, raising concerns about internet safety.
Microsoft released out-of-band updates to remove trust in eMudhra certificates after compromise of the certificate authority keys.
Scale AI faces five GDPR complaints in EU countries over allegations of unlawful worker surveillance on its Outlier AI platform.
Warp, an AI-powered development environment, suffered a breach exposing agent decision logs and user telemetry data through a third-party infrastructure vendor.
University of New Mexico's Health Sciences Center experienced a cyberattack on October 26, forcing the closure of clinics, cancellation of classes, and diversion of ambulances to nearby facilities.
A Congressional investigation reveals that the U.S. government lacks coordinated response mechanisms to combat rising cyberscams exploiting AI, with fragmented private-sector partnerships and poor victim restitution rates.
Surfshark reports that a fake TikTok shop is responsible for the majority of phishing attempts it blocked, with overall phishing blocks rising 83% over six months.
A critical vulnerability in Microsoft Authenticator for Android allowed malicious apps to steal account access credentials.
CISA has confirmed active exploitation of two critical PHP2Shell vulnerabilities and set an October 29 deadline for federal agencies to patch the bugs rated 9.2 on the CVSS scale.
U.S. government warns that hackers are exploiting critical vulnerabilities in PHP, the software used in 70% of web applications.
Tailscale has identified nearly a dozen security vulnerabilities that could enable credential theft, server crashes, and root privilege escalation, which the team is working to patch.